Internal security & credential platform
HAS Holding
Centralized multi-brand credential vault with encryption, access control and audit visibility.
A centralized internal system designed to replace fragmented credential spreadsheets and uncontrolled account sharing across multiple subsidiary brands.
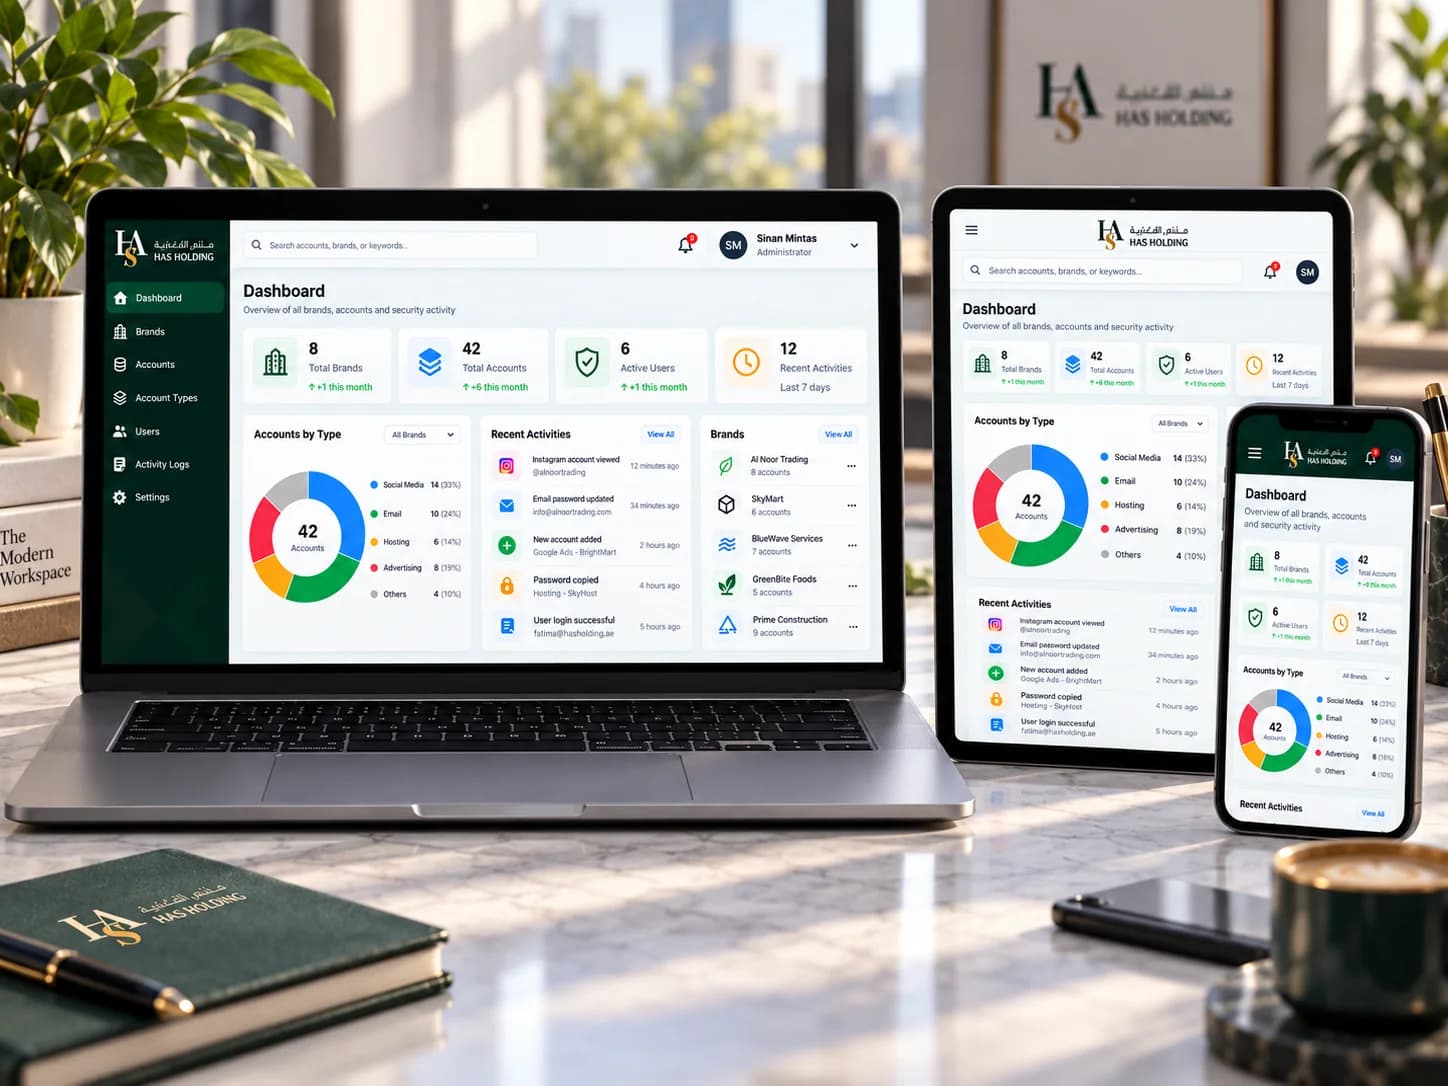
Holding companies accumulate social, email, hosting and advertising credentials across brands. Spreadsheets make it difficult to know who has access, what is current and when sensitive information was used.
We developed a Laravel-based multi-brand vault where credentials are grouped by brand and account type, sensitive data is encrypted, authorized roles control visibility and important access actions are logged.
The parts of the project that do the actual work.
Multi-brand architecture
Accounts are organized under the correct subsidiary brand.
Encrypted storage
Sensitive account information is encrypted at rest.
Role permissions
Users see only the accounts and actions required for their role.
Search & filter
Teams find accounts by brand and account type.
2FA & session security
Additional authentication protects vault access.
Audit trail
Access activity can be reviewed for accountability.
Account-type categorization
Social, email, hosting and advertising credentials are grouped by type for faster controlled access.
Security dashboard
Administrators can see brands, accounts and account distribution from one operating view.
The product and engineering decisions behind the result.
Mirrored the holding structure
The data model follows Holding → Brand → Account instead of a flat credential list.
Encrypted sensitive fields
Credentials are protected separately from ordinary account metadata.
Permission-first UX
Visibility and editing follow authorized roles rather than exposing every account to every user.
Auditability built in
Important actions become traceable events instead of invisible sharing through private messages.
From the first action to the outcome, the workflow stays connected.
Add brand
Admin creates the relevant subsidiary brand.
Store account
Credentials are categorized and saved securely.
Control access
Permissions define who may view, copy or edit.
Use & audit
Authorized access is logged for review.
Update securely
Credentials can be changed without uncontrolled spreadsheets.
Credential access becomes a controlled business process instead of an informal sharing habit.
The holding company gains one controlled workspace for digital credentials across brands, reducing dependency on personal spreadsheets and creating clearer accountability around account access.